Live detonation · public scan
We press the button so you don't have to.
Every URL you send us is opened in a real browser, on a throwaway copy of the page. We click what it wants clicked, record what it tries to hide, and hand you the evidence. Watch one happen.
Free · no signup needed for public scans
- 01PreflightWAIT
- 02Headless renderWAIT
- 03Interaction · throwaway copyWAIT
- 04Clipboard evidenceWAIT
- 05Reputation · 7 enginesWAIT
- 06Verdict · upward-onlyWAIT
Three numbered steps appear, asking the visitor to open the Run dialog, paste, and press Enter. Described here, never shown.
CLIPBOARD WRITE INTERCEPTED · HIDDEN FROM THE PAGE
What the engine caught this week
Every dot is a page that lied to someone.
Behind this panel is the last seven days of malicious public scans, drawn as they happened. Each one links to the report that convicted it. This is not an illustration; it is the product, running.
- MALICIOUS SCANS
- 0
- DISTINCT HOSTS
- 0
- COMMANDS CAPTURED
- 0
- BRANDS IMPERSONATED
- 0
Families
Most of it is the attack with no download.
ClickFix pages copy a hidden command to the clipboard and talk the visitor into running it. We press the gate on a throwaway copy and keep the command as evidence.
Commands captured
0 commands the victim was meant to run. None of them ran.
Captured inside an isolated browser, redacted on public pages, shown in full behind a hazard warning in the report.
Source: Urlyze public community feed, snapshot 2026-10-04T11:25Z. Dots per day are real; a dot's position within its day is not. Hosts defanged.
Evidence, not a score
Every scan ends in a report you can hand to someone.
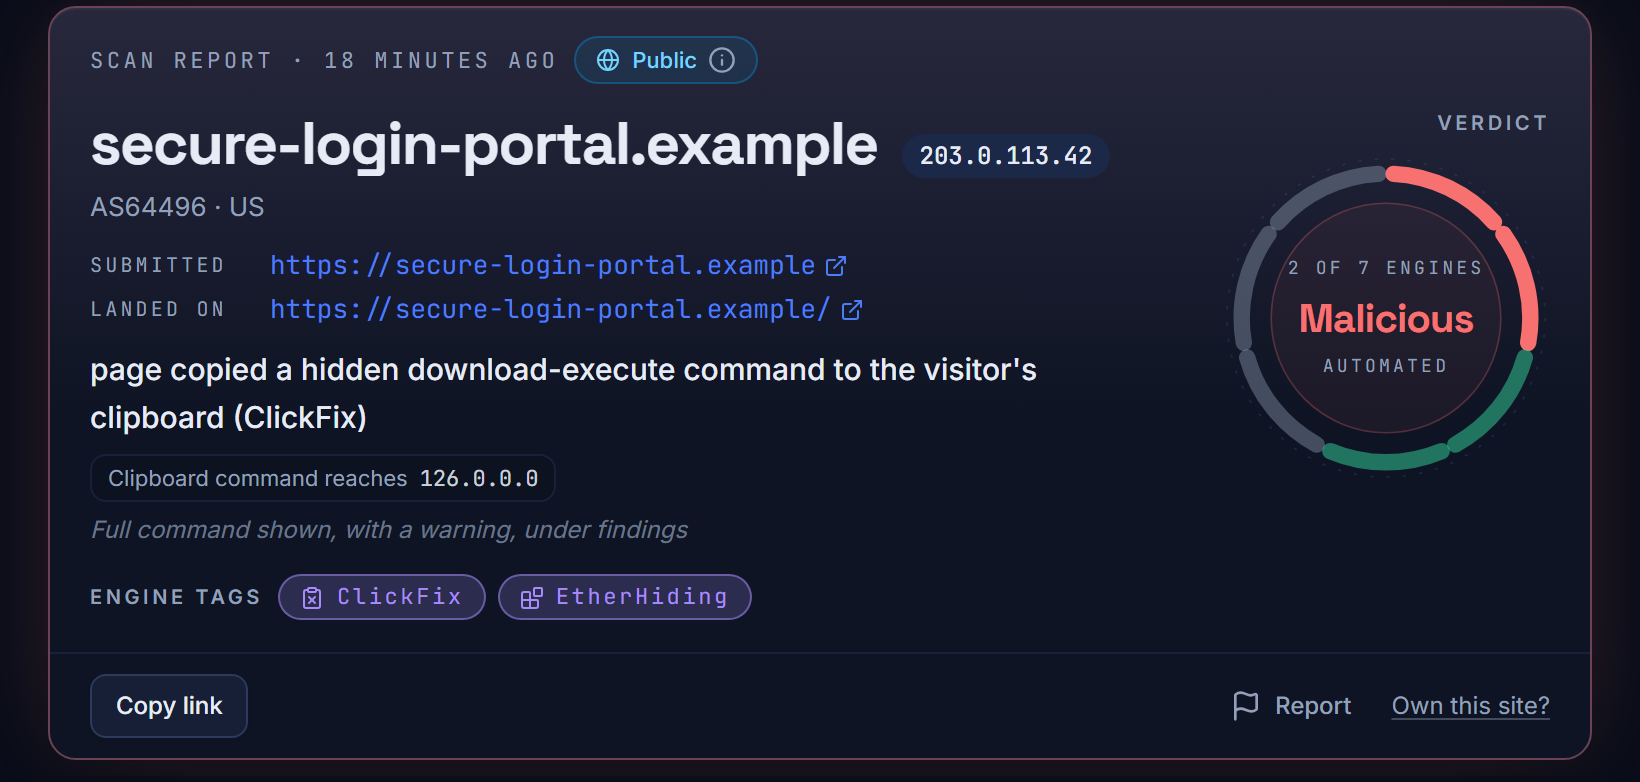
A verdict, the explanation behind it, an analyst hint, every engine's answer, the redirect chain, the screenshots, the captured command. Private by default; yours to export.
- Clean, Suspicious or Malicious, with the reasoning attached
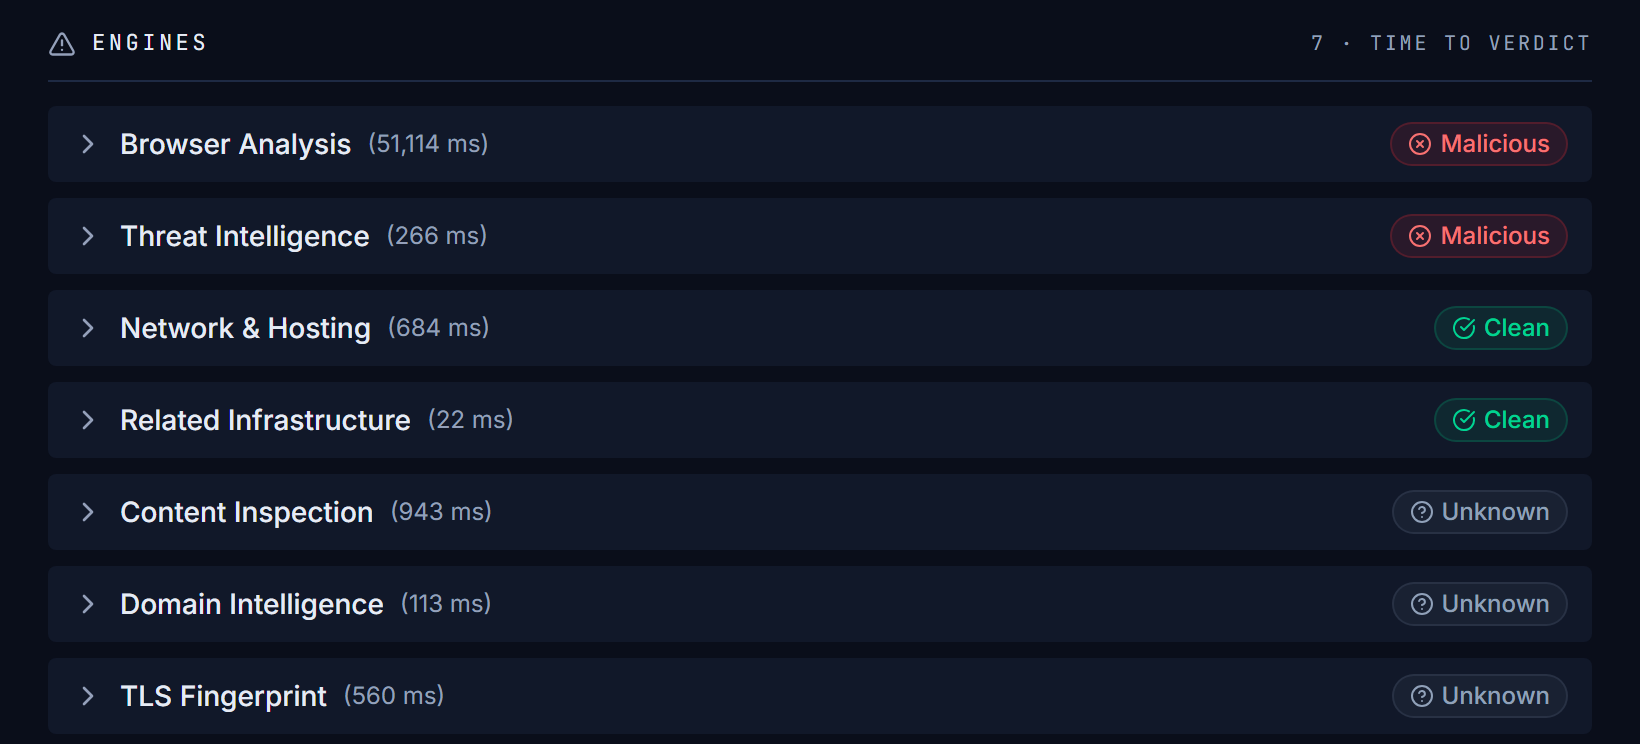
- Seven engines, each with its own verdict and time to verdict
- IOC / STIX export, takedown evidence pack, case handoff
Brand protection · URL analysis
Everything on this page looks fine.
A login link from your bank. A verification step. An invoice from a supplier you know. The web is built to look trustworthy, and attackers build on the same web.
What it is
Nothing on this page is what it says.
The lens is the product. Every scan opens the page in a real browser, presses what it wants pressed, and records what it hides from you. The gap between the two layers is the finding.
~70,000 newly registered domains a day
We read every one of them for your name.
The phishing site that doesn't exist yet.
A lookalike with mail servers configured and no website is a BEC attack waiting to happen. Site-only scanners can't see it. Urlyze flags it the day it's registered, days before the first email.
Brand & domain protection- MX configured
- SPF published
- Website none
Platform
Four pillars, one evidence trail.
URL Scanning & Analysis
A real browser, a throwaway copy, a verdict with the explanation and analyst hint that justify it.
Learn more 02Brand & Domain Protection
Lookalikes over ~70,000 new registrations a day, BEC-capable alerts, takedown evidence packs.
Learn more 03Email Security Posture
SPF, DKIM, DMARC, BIMI, MTA-STS and TLS-RPT graded on the domains you own, with downgrade alerts.
Learn more 04SOC Workflow
Cases, IOC/STIX export, SIEM integration, scheduled monitoring. Everything in the UI is in the API.
Learn moreTrust & privacy
Built to be trusted with what you scan.
- Submissions private by default
- Credentials and secrets stripped at capture, never stored
- Strict tenant isolation
- Hosted in the EU
- Served through Cloudflare's global edge
Browser extension
Urlyze — Scan Before You Click
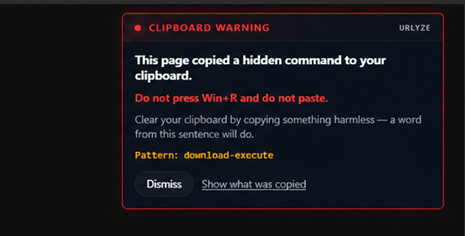
Scan the page you're on, or any link on it, before you click. It warns at the moment a page writes to the clipboard, before the paste, when a warning is still useful. It does not read your pages; it acts when you ask it to.
Know before you click