Platform
One platform, four pillars.
From the first suspicious URL to the takedown request, every step backed by a full forensic scan.
01 · URL scanning
URL Scanning & Analysis
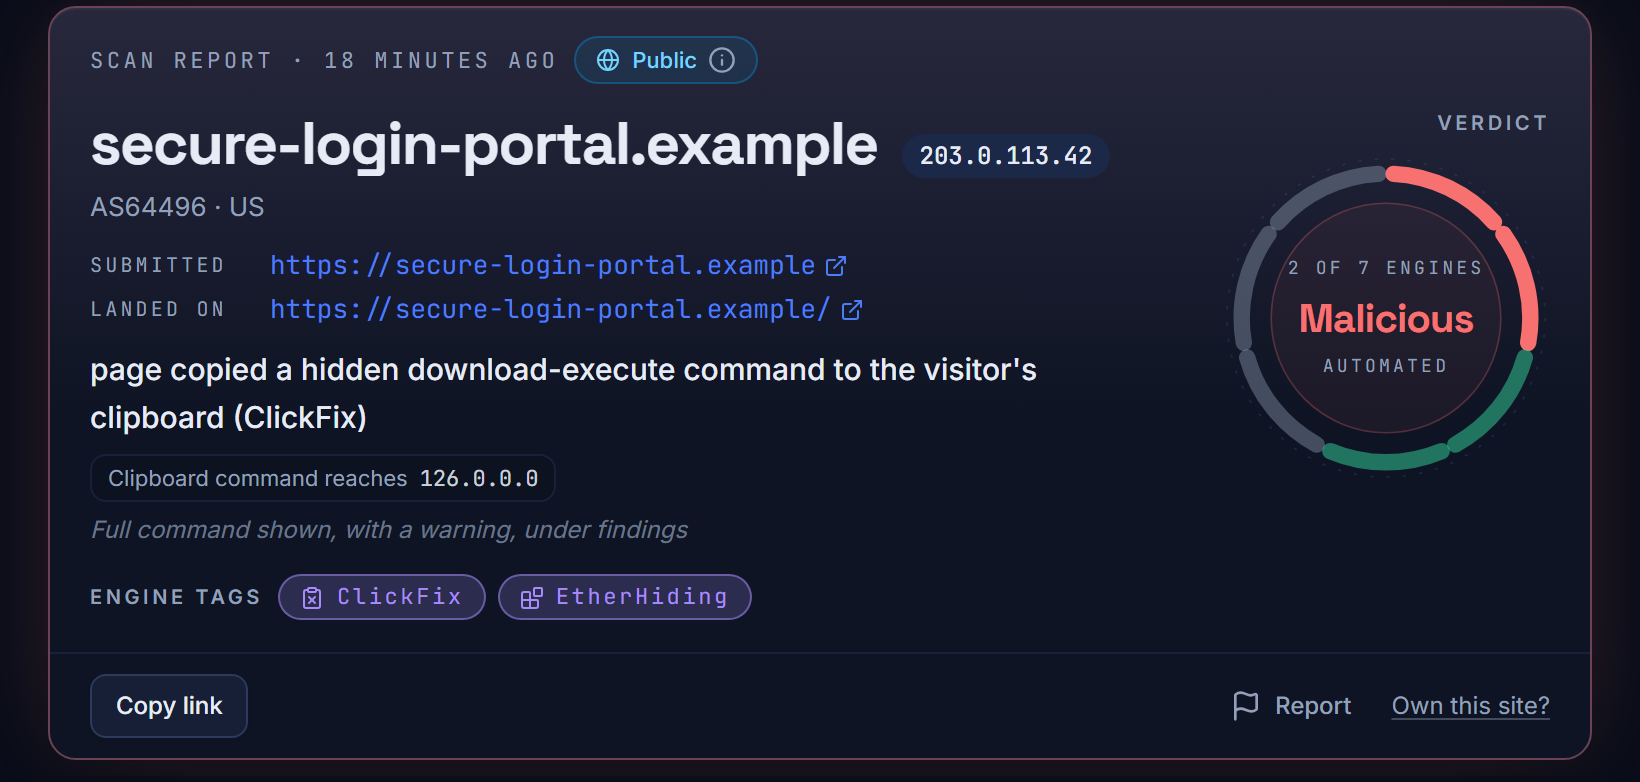
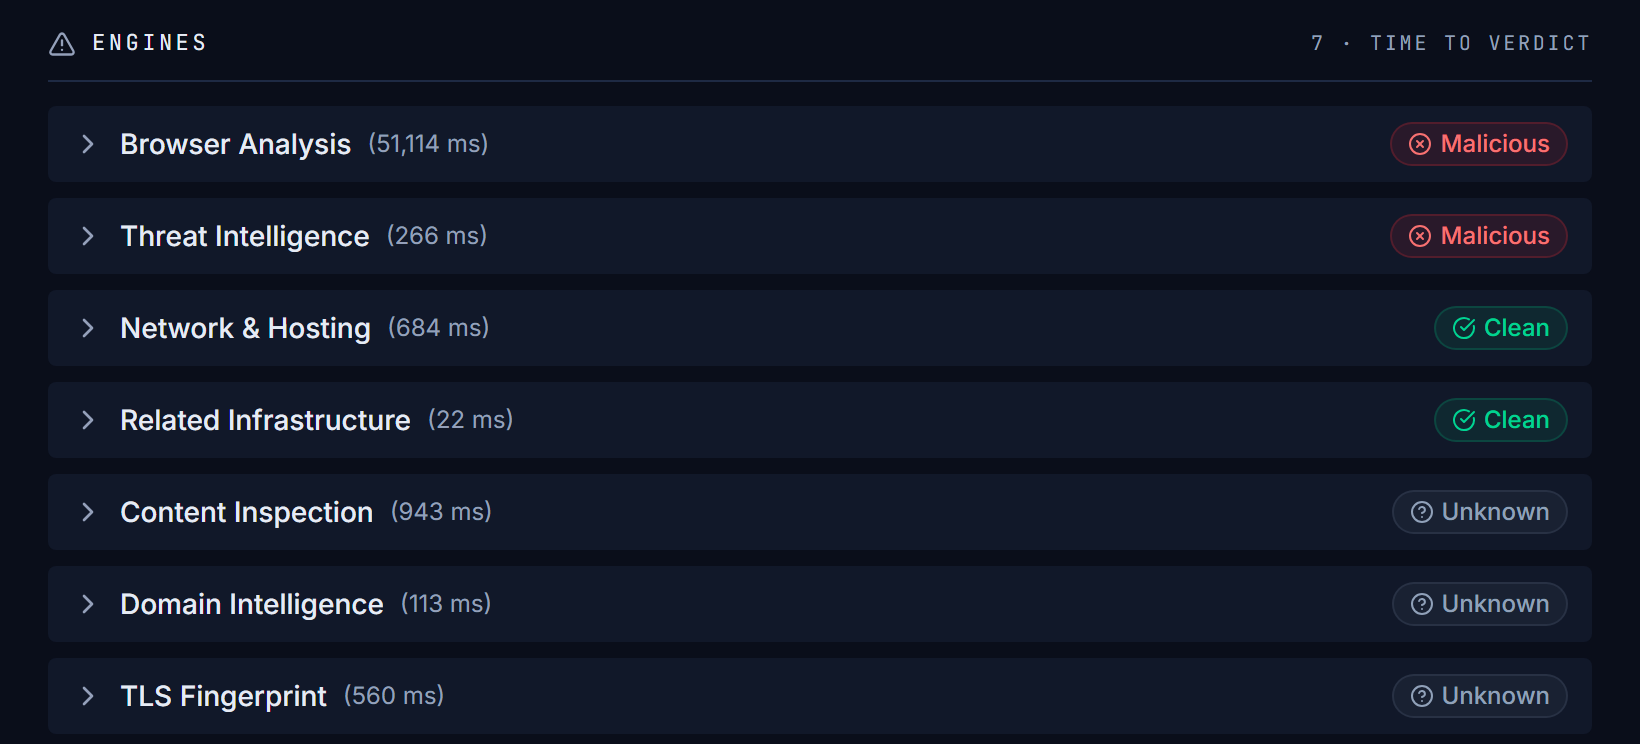
A real browser loads the page. The scan ends in Clean, Suspicious or Malicious, with the explanation and analyst hint that justify it.
- Redirect chain, DOM forensics and multi-stage screenshots from a headless browser
- ClickFix, EtherHiding and executable-delivery detection, pressed on a throwaway copy of the page
- Multi-engine reputation plus file and document analysis
- Cloaked, CAPTCHA-gated redirectors, scanned from the egress region you choose
02 · Brand protection
Brand & Domain Protection
Lookalike and typosquat discovery over ~70,000 newly registered domains a day, with the evidence to take them down.
- Impersonation caught by visual and phishing-kit fingerprints, even when the domain looks unrelated
- BEC-capable alerts: mail-armed lookalikes with no website, flagged the day they are registered
- Inventory classified live / parked / mail-armed, so you know what to act on first
- Takedown evidence packs backed by the full forensic scan
Lookalike inventory · urlyze.io
- ur1yze.iolive
- urlzye.ioparked
- urly2e.ioBEC-capablemail-armed
- urlyze-io.comparked
03 · Email posture
Email Security Posture
Grade and watch the email authentication of the domains you own.
- SPF, DKIM and DMARC graded on every owned domain
- BIMI, MTA-STS and TLS-RPT checked alongside
- Downgrade alerts when a domain's posture slips
- SPF-all
- DKIMaligned
- DMARCp=reject
04 · SOC workflow
SOC Workflow
Built for how analysts actually work: API-first, with the exports and integrations your stack expects.
- Cases from first alert to closure, in one place
- IOC / STIX export and SIEM integration
- Everything in the UI available over the API
- Scheduled monitoring, saved searches and Telegram brand mentions
- Report intake: a forwarded suspicious email lands in your workspace already scanned
Case · lookalike takedown
- Alert
- Triaged
- Evidence pack
- Takedown requested
Pipeline
How a scan runs.
Every URL moves through the same pipeline. A step can raise the verdict's severity, never lower it.
- 01PreflightRUN
- 02Headless render
- 03Interaction & clipboard evidence
- 04Reputation engines
- 05Content & document analysis
- 06Fingerprint & correlation
- 07Verdict
- 08Evidence
Step 01
Preflight
DNS resolution and TCP reachability, so dead domains fail fast instead of burning a scan.
resolve · tcp/443 · 41 ms
Step 02
Headless render
A real browser loads the page: redirect chain, DOM, multi-stage screenshots.
chromium · 1 hop · 37 requests · screenshot #1
Step 03
Interaction & clipboard evidence
Gates and prompts are pressed on a throwaway copy of the page, capturing what it writes to the clipboard and the screen that only appears afterwards.
gate pressed on copy · clipboard.writeText intercepted · screenshot #2
Step 04
Reputation engines
Multiple reputation engines queried in parallel.
7 engines · parallel
Step 05
Content & document analysis
In-depth inspection of files and documents met during the scan.
files · documents · deep inspection
Step 06
Fingerprint & correlation
Phishing-kit fingerprints, brand-baseline matching, correlation rules.
kit fingerprint · brand baseline · correlation
Step 07
Verdict
Signals aggregate upward-only. A step can raise severity, never lower it, ending in a verdict with its explanation and analyst hint.
suspicious → malicious · explanation · analyst hint
Step 08
Evidence
Full report, IOC/STIX export, takedown evidence pack, case handoff.
report · IOC/STIX · evidence pack · case
API
Built API-first.
Submit scans and poll verdicts, pivot across fingerprint dimensions, fetch screenshots, export IOC feeds as JSON, STIX 2.1 or EDL lists. Everything the platform does is available over the API.